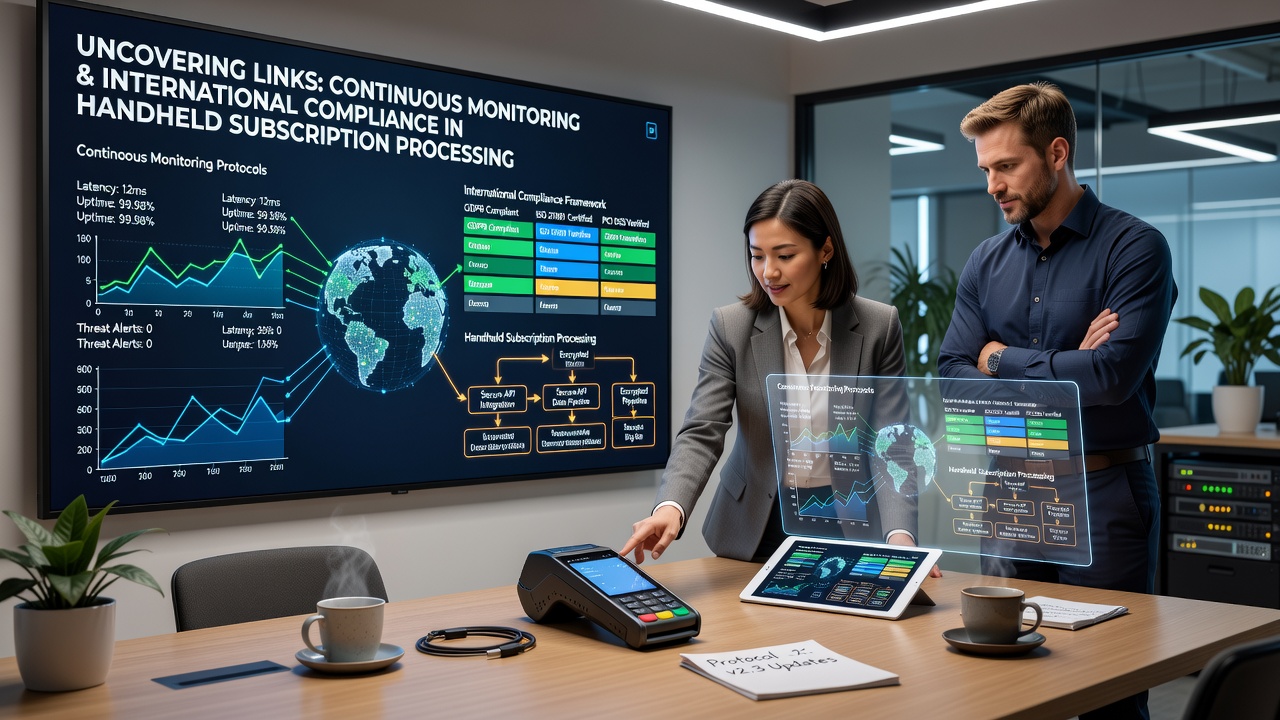
Mapping Connections Between Persistent Oversight Systems and Worldwide Regulatory Frameworks in Mobile Subscription Handling
Continuous monitoring protocols operate as real-time surveillance layers that track transaction patterns, user behaviors, and system anomalies in portable subscription services, while international compliance frameworks set the rules that these systems must satisfy across borders. Researchers at various institutions have documented how these two elements intersect when companies process recurring charges on smartphones and tablets, particularly in regions where data protection laws and payment security standards overlap. Data from industry reports shows that organizations implementing both elements together report fewer disruptions during audits conducted by multiple jurisdictions simultaneously.
Defining the Core Components in Practice
Persistent oversight systems collect streams of data from application programming interfaces that handle subscription sign-ups, renewals, and cancellations on handheld devices, then apply algorithms to flag deviations from established baselines. International rules such as the European Union's revised Payment Services Directive and Canada's guidelines on electronic payments require documented evidence that these oversight systems maintain consistent performance regardless of where the transaction originates. Observers note that companies must demonstrate audit trails that satisfy both local regulators and foreign authorities when subscriptions cross national boundaries, which often means aligning monitoring thresholds with the strictest applicable standard.
Standards bodies publish updated specifications at regular intervals, and one update scheduled for release in August 2026 will introduce new requirements for encryption verification during variable-cycle billing on mobile platforms. Those who manage handheld subscription flows have already begun mapping their current monitoring setups against the anticipated changes to avoid gaps when the new rules take effect.
How Monitoring Protocols Support Compliance Verification
Continuous monitoring feeds directly into compliance reporting by generating timestamped logs that regulators can review without requesting separate data pulls. When a handheld subscription service operates across teh United States, the European Union, and Australia, each jurisdiction expects evidence that the same monitoring rules apply uniformly, yet each may emphasize different risk indicators. Figures from cross-border payment studies reveal that firms using unified monitoring dashboards reduce the time required to produce jurisdiction-specific reports by measurable percentages compared with fragmented approaches.
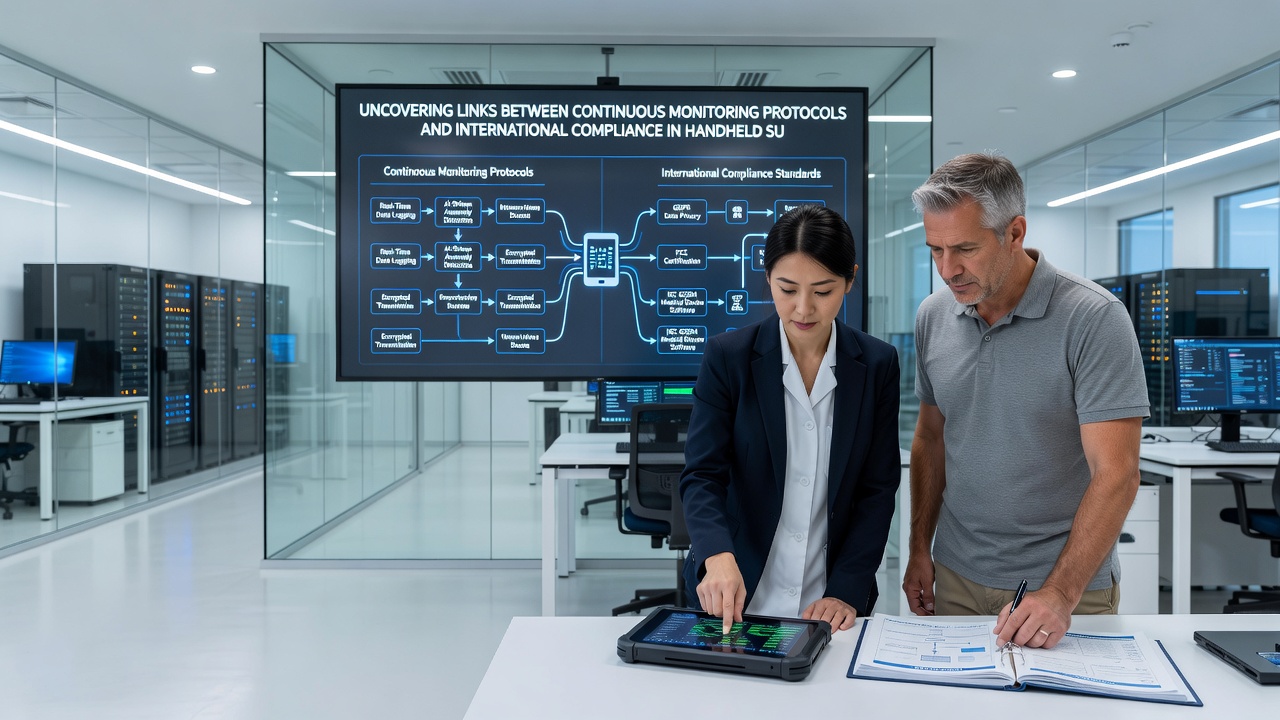
One documented case involved a service provider that adjusted its anomaly detection thresholds after European regulators highlighted inconsistencies with data minimization principles under GDPR, while simultaneously meeting U.S. expectations for fraud pattern retention. The adjustments occurred through a single monitoring platform rather than separate regional tools, which simplified both internal reviews and external examinations.
Technical Integration Points Across Regions
Application interfaces that power recurring mobile billing now incorporate compliance checkpoints at the point of data capture, allowing monitoring protocols to evaluate each transaction against multiple rule sets in sequence. According to documentation released by the PCI Security Standards Council, organizations that embed these checkpoints report higher rates of sustained certification when they also maintain continuous oversight of encryption status and access controls. Similar guidance appears in materials from the European Central Bank, which stresses that monitoring must cover the entire lifecycle of a subscription rather than isolated events.
Handheld environments introduce additional variables such as operating system updates and device-level permissions, so monitoring protocols must account for these factors without violating retention limits set by different countries. Experts who have examined multiple implementations observe that modular monitoring architectures permit selective activation of regional rules while preserving a common core of data collection practices.
Conclusion
The relationship between continuous monitoring protocols and international compliance in handheld subscription processing rests on shared data requirements and synchronized reporting mechanisms. Organizations that align these elements through integrated platforms produce verifiable records that satisfy overlapping regulatory demands without duplicating infrastructure. As specifications evolve, including the changes slated for August 2026, the same monitoring systems that detect operational issues also generate the evidence needed to demonstrate adherence across borders.